Security Concepts & Threat Analyses12 min read
Resilience Evidence for the BBK: Making It Audit-Ready
Evidence is built in the derivation, not at the end: if you cannot derive a protective measure from a documented threat and risk analysis, you have no audit-ready justification. This article shows the documentation chain that survives the evidence check under the KRITIS Umbrella Act.
Key Takeaways
- The KRITIS Umbrella Act entered into force on 17 March 2026 and, for the first time, regulates physical resilience under a single federal standard.
- The resilience plan must show the considerations behind every measure, with reference to the risk analysis (Section 13(4)).
- The risk analysis must be repeated at least every four years; the resilience plan must then be updated (Sections 12 and 13).
- The authority requests evidence on a risk basis, including by requiring the resilience plan and audits (Section 16).
- Equivalent evidence from other legal obligations can be recognised (Section 17).
The new legal framework: physical resilience under the KRITIS Umbrella Act
The KRITIS Umbrella Act (KRITIS-Dachgesetz) transposes the CER Directive (EU) 2022/2557 into German law and entered into force in March 2026. It creates, for the first time, a uniform, nationwide and cross-sector legal framework for the physical protection of critical facilities. Alongside the IT security duties under the BSIG, operators now face a second, independent set of duties: physical resilience.
- Scope boundary: cyber defence requirements continue to be governed by the BSI Act as part of the NIS2 transposition. The KRITIS Umbrella Act additionally sets independent minimum requirements for the physical protection of critical facilities.
- Scope: the decisive factor is the standard threshold of 500,000 inhabitants supplied.[1] Which facilities and services are covered in detail is determined by an ordinance of the Federal Ministry of the Interior that has yet to be issued.
- Deadlines: operator duties begin with registration. The first risk analysis is due nine months after registration, the first resilience duties ten months after registration.[2]
For providing evidence, this leads to a practical finding: the deadlines run from registration, not from the act's entry into force. Anyone who plans to set up their own risk analysis and resilience plan only when the supervisory authority first requests documents uses up the preparation time the act expressly grants. The documentation that carries this evidence, by contrast, is not created at the end of the process but in its derivation. That is what the following sections are about.
What the evidence is meant to prove
The evidence provided to the Federal Office of Civil Protection and Disaster Assistance (BBK) and the competent authorities does not examine the facility as such, but its justification. The act makes this expectation explicit: operators must set out their resilience measures in a resilience plan that shows the considerations on which the measures are based, with reference to the risk analysis and assessment.[2]
- Resilience plan (Section 13(4) KRITIS-DachG): the plan documents the measures and discloses the considerations from which they are derived, with explicit reference to the risk analysis.[2]
- Proportionality as the yardstick: the act requires suitable and proportionate technical, security-related and organisational measures. Every measure must therefore justify itself against the risk it addresses.
- The authority's power to demand evidence (Section 16): the competent authority can request further evidence on a risk-based approach, including submission of the resilience plan as well as audits and inspections. The BBK specifies their type and conduct.[3]
This leads to the central conclusion of this article: a list of installed systems proves nothing. It shows which technology is installed, but not which risk required which measure, why an alternative was rejected, or why the chosen scope is proportionate. These are exactly the considerations the wording of the act requires. Anyone who has not documented them has no audit-ready justification, only an inventory.
The chain of derivation from threat and risk analysis to measure
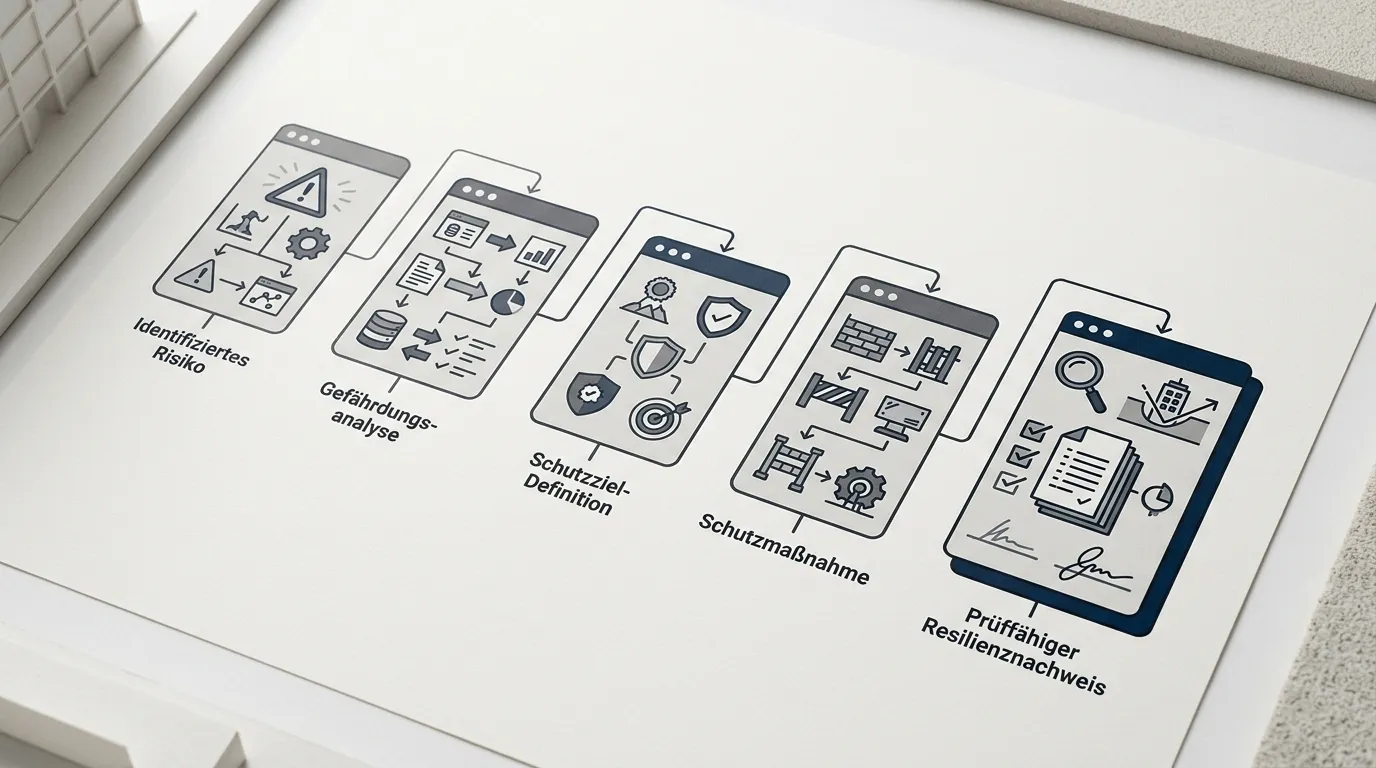
Evidence is built in the derivation. Every protective measure in the resilience plan must be traceable, in an unbroken chain, back to a documented risk. In our specialist planning this chain passes through four methodological steps, which can be used directly as the structure of your own documentation.
- As-is survey and needs analysis: processes, sites and workflows are recorded systematically. Without a reliable picture of what exists, it is impossible to justify later why this particular area is being protected (Security Concepts & Threat Analyses).
- Definition of protection objectives and risk assessment: threats are assessed quantitatively and qualitatively and protection objectives are defined. Particularly vulnerable areas are identified and prioritised.
- Catalogue of measures and target concept: the catalogue of measures is derived from the protection zone concepts. Each measure is given a documented assignment to the risk it addresses. The result is a multi-page target concept as the basis for decision-making.
- Planning, tendering and quality assurance: only on this basis is the detailed technical planning produced, from perimeter protection via video surveillance and access control to the higher-level security management system, and from it the manufacturer-independent specification of services (Specialist Planning for Critical Infrastructure).
We document the derivation of every measure from the threat and risk analysis, so that protection follows the risk, not a supplier's product catalogue. In an audit, this detachment from product logic is not a matter of style but the core of the evidence: the authority assesses the relationship between ends and means, and that relationship can only be read if the objective was documented before the means. Documentation that carries this chain is therefore also the basis for the later, product-neutral tender for the specific system technology.
What belongs in the documentation
From the wording of the act and the methodological chain above, it is possible to specify which components the documentation must contain to survive an audit. What matters is less the volume than the traceable links: every document must have its place in the derivation.
- Threat and risk analysis as the starting point, with quantitative and qualitative risk assessment and identification of particularly vulnerable areas.
- Definition of protection objectives and protection zone concepts, showing which level of protection is sought for which area.
- Catalogue of measures and multi-page target concept as the consolidated basis for decision-making.
- Assignment of every individual measure to its risk, including the documented consideration of why this measure was chosen and not another.
- Versioning and update status of every document, so that the authority can trace which version corresponds to which risk analysis.
As to form: no later than eight months after the ordinance enters into force, the BBK will publish non-binding models and templates for resilience plans on its website.[2] These templates set the outer structure. They do not, however, replace the derivation that has to be entered into them. Anyone who only starts filling in the templates once they are published does not yet have the content; anyone who already maintains the chain of risk, protection objective and measure simply transfers it into the prescribed format.
Cycle: when evidence is provided and updated
The statutory rhythm translates directly into operational planning. The following deadlines and cycles come from the text of the act and should appear as fixed dates in the calendar of those responsible for security, not as rough estimates.
| Duty | Provision | Cycle or deadline |
|---|---|---|
| Risk analysis and assessment | Section 12(1) KRITIS-DachG | at least every four years, additionally as required |
| Resilience plan | Section 13(4) KRITIS-DachG | update as required and after every risk analysis |
| Evidence to the authority | Section 16(2) KRITIS-DachG | no fixed cycle: evidence and the resilience plan on request from the authority, which selects operators on a risk-based approach |
| Requirements for evidence and audits | Section 16(8) KRITIS-DachG | the BBK specifies their type and conduct by public notice |
This suggests three fixed dates in operational planning. First, a risk review every four years with clearly assigned responsibility, supplemented by defined triggers, such as significant changes to sites, facilities or processes, that prompt an earlier update. Second, a scheduled revision of the resilience plan after every risk analysis, so that the plan is never older than the analysis it refers to. Third, a regular internal review of the evidence documents: as the act sets no fixed evidence cycle, but the authority can request evidence at any time on a risk basis, the documentation should always be ready to submit.[4] Documenting these dates also proves that the update process itself is actually lived.
Working with authorities, expert assessors and auditors
Whoever prepares the documents should know who will read them. The KRITIS Umbrella Act spreads supervision across several levels: at federal level the BBK is the national competent authority within the meaning of the CER Directive, while the sector authorities and the federal states remain responsible alongside it. The inspection itself can be delegated to third parties.
- Inspection by third parties: the competent authority can also have compliance with the requirements checked by qualified independent third parties; these must be granted access to premises and insight into systems and documents.[3]
- Equivalence: risk analyses, assessments, documents and measures prepared under other legal obligations or voluntarily can be used as evidence. Findings of other authorities on them are binding in the operator's favour.[2]
- Remedying deficiencies: if the authority identifies deficiencies, it can require them to be remedied and a remediation plan and corresponding evidence to be submitted.[3]
This readership expects a traceable derivation and audit-ready documentation, not a collection of manufacturer data sheets. That is exactly what our collaboration in the KRITIS field is geared to: we work closely with operators' security managers, the authorities and the expert assessors, and document the derivation of every measure from the threat and risk analysis. The equivalence rule in Section 17 relieves everyone who already documents under other legal obligations: existing analyses and concepts do not have to be produced twice; they only need to be prepared in an audit-ready form and assigned to the chain of derivation.
Audit-ready documentation with independent specialist planning
An audit under the KRITIS Umbrella Act is not a question of the system list, but of the derivation. Anyone who can derive every measure from a documented threat and risk analysis answers the questions of the authority, the expert assessors and the auditors from their own documentation. Anyone who cannot has no gap in their evidence, but a gap in their concept.
- Security concepts and threat and risk analyses as the preliminary phase of every planning project, with documented definition of protection objectives and risk assessment.
- Specialist planning of security technology from perimeter security via video surveillance and access control to the higher-level security management system, manufacturer-independent and coordinated.
- Manufacturer-independent tendering and site supervision through to acceptance, so that the documented derivation carries through into the specification of services and the installation.
As an independent engineering and planning firm, we are committed solely to your protection objectives and plan without ties to manufacturers or service providers. On our page on Specialist Planning for Critical Infrastructure (KRITIS) you will find an overview of our services for operators, from the threat and risk analysis via the planning of security technology to the manufacturer-independent tender and site supervision. We support operators in energy supply, municipal drainage and aviation, among others, and align our concepts with your security managers, the authorities and the expert assessors.
Contact us for a no-obligation initial consultation. PLANATEL®: Independent planning and consulting since 1992. Tel: 040 / 23 73 02-30 | Email: info@planatel.de
Frequently Asked Questions
To whom must resilience evidence under the KRITIS Umbrella Act be provided?
The respective competent authority is responsible; at federal level the BBK is the national competent body. Under Section 16 KRITIS-DachG, the authority can, via the BBK, ask the BSI for access to relevant parts of existing evidence, request further evidence on a risk basis and require submission of the resilience plan. For operators in electricity, gas and hydrogen, Section 5f of the Energy Industry Act (EnWG) applies instead (Section 16(7)).
How often must the risk analysis under the KRITIS Umbrella Act be carried out?
The operator carries out the risk analysis and risk assessment as required, but at least every four years (Section 12(1) KRITIS-DachG). The resilience plan must be updated as required and after every risk analysis carried out (Section 13(4)). The act sets no fixed evidence cycle: the authority requests evidence on a risk basis (Section 16(2)); the BBK specifies its type and conduct by public notice (Section 16(8)).
What belongs in the resilience plan?
The resilience plan sets out the resilience measures and is applied. It must show the considerations on which the measures are based and refer to the operator's risk analysis and risk assessment (Section 13(4) KRITIS-DachG). No later than eight months after the ordinance enters into force, the BBK will provide non-binding models and templates.
From when do the duties for operators of critical facilities apply?
The duties begin after registration: the first risk analysis is due nine months after registration, and the resilience duties, reporting and management's implementation duty ten months after registration (Section 8(7) KRITIS-DachG). The registration duty only arises once the identification ordinance has entered into force; the BBK recommends that operators start addressing resilience now.
Can existing threat and risk analyses be recognised as evidence?
Yes. Under Section 17 KRITIS-DachG, risk analyses, risk assessments, documents, measures and certificates that the operator has prepared or obtained under other legal obligations or voluntarily can be used as evidence. Findings of other authorities on them are binding in the operator's favour. The precondition is that the derivation of the measures is documented and audit-ready.
What does the authority check during an on-site inspection?
Under Section 16(4) KRITIS-DachG, the competent authority can check compliance with the resilience duties and use a qualified independent third party to do so. The operator must permit entry to business and operating premises as well as access to information, systems and facilities, and must submit records, written documents and other materials. If there are deficiencies, the authority can order a remediation plan within a reasonable period (Section 16(5)).
What role does management play in resilience evidence?
Under Section 20 KRITIS-DachG, management is obliged to implement the resilience measures and to ensure their implementation through suitable organisational measures. For the documentation this means that responsibility for preparing, updating and submitting the resilience plan must be assigned bindingly within the organisation.
Sources
- KRITIS-Dachgesetz: Neuer bundeseinheitlicher Rechtsrahmen für den physischen Schutz kritischer Infrastrukturen tritt in Kraft – GÖRG
- KRITIS-Dachgesetz (KRITISDachG) – buzer.de
- KRITIS-Dachgesetz: Was Unternehmen jetzt wissen und tun müssen – IHK Köln
- § 16 KRITISDachG – gesetze-im-internet.de
- KRITIS-Dachgesetz – OpenKRITIS