Security Concepts & Threat Analyses14 min read
KRITIS Umbrella Act: Physical Protection Duties and Deadlines
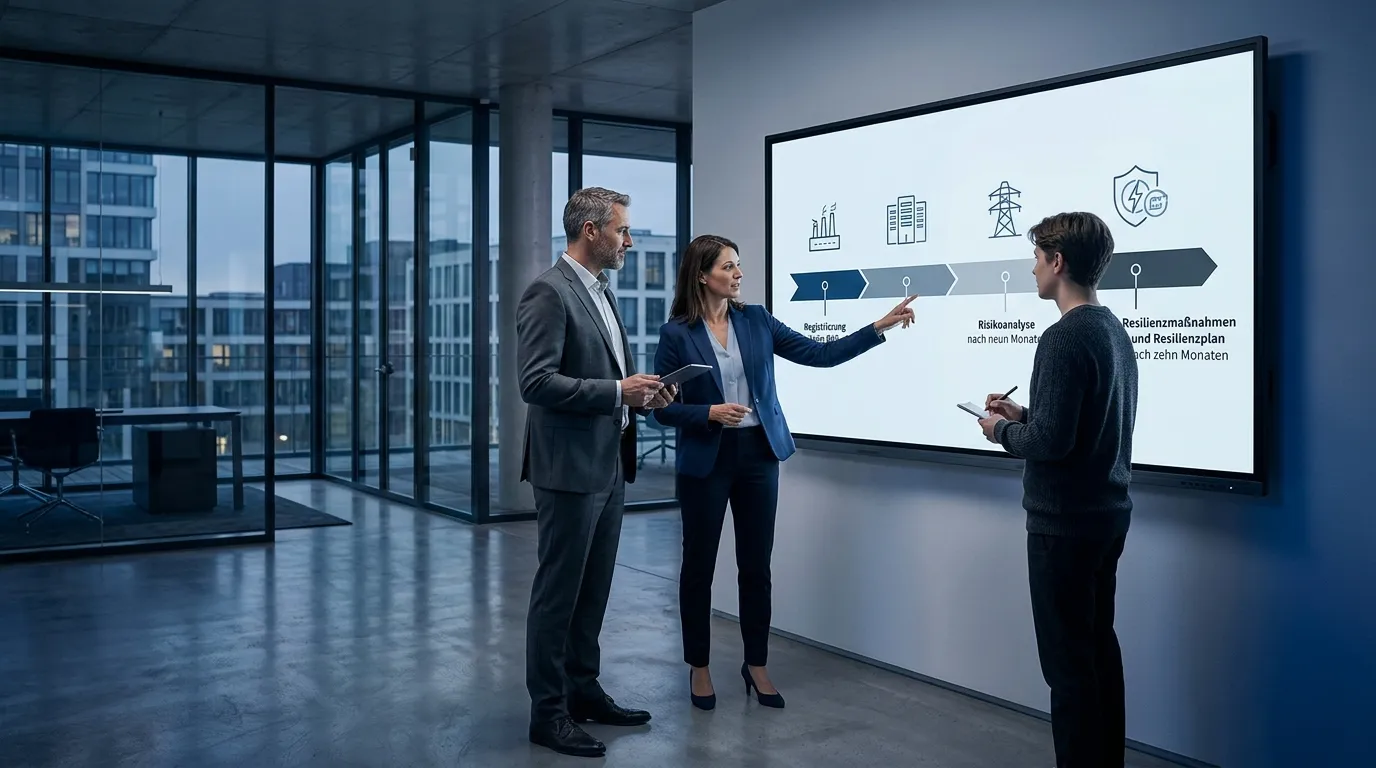
The KRITIS Umbrella Act has been in force since 17 March 2026 and, for the first time, requires appropriate physical protection of critical facilities under a single federal standard. We translate the duties into a timeline that starts at registration: risk analysis after nine months, resilience measures after ten.
Key Takeaways
- The KRITIS Umbrella Act (KRITIS-Dachgesetz) entered into force on 17 March 2026 and, for the first time, sets a single federal standard for the physical protection of critical facilities.
- Deadlines run from registration: the first risk analysis is due after nine months, the first resilience measures and resilience plan after ten months.
- The registration date of 17 July 2026 was struck by an amendment of 29 July 2026; the three-month period now starts with the KRITIS ordinance.
- Section 13 names types of measures such as site perimeter boundaries, monitoring of the surroundings, detection devices and access controls, which must be derived on a risk basis and in proportion.
- The cyber duties under the BSI Act and NIS-2 do not cover the physical duties; breaches of the KRITIS Umbrella Act can be punished with fines.
Since when the KRITIS Umbrella Act applies
The KRITIS Umbrella Act entered into force on 17 March 2026. It creates, for the first time, a uniform federal, cross-sector legal framework for the physical protection of critical facilities. For operators this means that the duties under this act run in parallel with the familiar IT security duties; they do not replace them.
The European background is Directive (EU) 2022/2557 on the resilience of critical entities, the CER Directive. It entered into force on 16 January 2023 and obliged the member states to introduce binding minimum standards for the physical protection of critical entities. The transposition deadline ended on 17 October 2024; the delayed transposition led to infringement proceedings against the Federal Republic of Germany.
- Entry into force: 17 March 2026, after adoption by the Bundestag on 29 January 2026 and consent of the Bundesrat on 6 March 2026
- European basis: CER Directive (EU) 2022/2557, with a transposition deadline of 17 October 2024
- Scope boundary: IT security duties are already governed by the BSIG and the NIS-2 Implementation Act; the KRITIS Umbrella Act regulates physical resilience in its own right
The clear separation of the two protection domains is essential for your planning: while the IT security requirements are covered by the BSI Act, the KRITIS Umbrella Act sets, for the first time, independent, federally uniform minimum requirements for the physical protection of critical facilities. At the same time, the previous ordinance determining critical facilities under the BSI Act (BSIKritisV) is repealed; classification will in future follow the Umbrella Act's own framework.
Which facilities and operators the act covers
Before you draw up deadlines, you need to know whether your facility falls within scope at all. The deadlines depend on classification as a critical facility, not on a calendar date. The act applies to operators of critical facilities in ten sectors under Section 4(1) KRITIS-DachG.
- Energy
- Transport and traffic
- Finance
- Social insurance and basic income support
- Healthcare
- Water (drinking water and wastewater)
- Food
- Information technology and telecommunications
- Space
- Municipal waste disposal
| Classification level | What is determined |
|---|---|
| Act (Section 5(1) to (2)) | Standard threshold: supply to, as a rule, 500,000 inhabitants as the yardstick for classification |
| Ordinance of the Federal Ministry of the Interior (Section 4(3), Section 5(1)) | Specific critical services and thresholds; so far only available as a draft, entry into force was expected for summer 2026 |
| Federal states (Section 5(7)) | State opening clause: the federal states may designate further critical facilities and services within their remit |
Alongside the quantitative threshold, qualitative factors feed into classification, such as dependencies, market share and potential impact of damage. As the ordinance that gives the act its detail is still pending, you should prepare your self-assessment now on the basis of the threshold and these qualitative criteria, rather than leaving the question of whether you are affected open.
Which duty applies from which date
The duties under the KRITIS Umbrella Act form a chain whose first link is registration. An important update first: the originally stated date of 17 July 2026 as the start of the period was struck by an amendment of 29 July 2026. The three-month registration period now starts only when the ordinance determining critical facilities enters into force, because registration depends on that determination. The date of 17 July 2026 is therefore void as a running deadline.[1]
Striking a date is not a suspension of the act. The KRITIS Umbrella Act remains in force; only the starting point of the timeline has moved, because the further duties are tied to registration[2]. From the individual registration date, the timeline looks like this:
| Point in time | Duty | Legal basis |
|---|---|---|
| No later than three months after a facility is deemed a critical facility (period starts when the KRITIS ordinance enters into force) | Registration with the BBK via the joint BBK and BSI platform, including details of the operator, the facility, the supply area and a contact point that can be reached at all times | Section 8(1) KRITIS-DachG |
| Nine months after registration | First risk analysis and risk assessment | Section 8(7) in conjunction with Section 12 KRITIS-DachG |
| Ten months after registration | First resilience measures and resilience plan (Section 13), reporting duties (Section 18) and management duties (Section 20) | Section 8(7) KRITIS-DachG |
| Ongoing | Update the risk analysis at least every four years, earlier in the event of significant changes; submit evidence at the supervisory authority's request; report significant disruptions without delay, at the latest within 24 hours | Sections 12, 16 and 18 KRITIS-DachG |
For your deadline framework this means: take your own registration date as day zero and plan in the nine months to the first risk analysis from the outset. The risk analysis is the most demanding preliminary stage of the resilience plan, and a resilience plan cannot be produced at short notice when the supervisory authority asks for it[2]. Breaches of central duties can be punished as administrative offences with substantial fines.
What Section 13 means by appropriate physical protection
Section 13 KRITIS-DachG sets out the resilience duties through four objectives. The operator is obliged to take measures in accordance with subsections 2 and 3 to achieve these objectives[3]:
- to prevent incidents from occurring
- to ensure appropriate physical protection of sites and critical facilities
- to respond to incidents, repel them and limit their negative effects
- to ensure the swift restoration of the critical service after incidents
For objective number 2, appropriate physical protection, subsection 3 number 2 names the types of measures that may count towards it: structural and technical security measures and organisational protection (property protection) such as site perimeter boundaries and resistant façade elements, instruments and procedures for monitoring the surroundings, the use of detection devices, and access controls[3]. The wording "may count" is deliberate: this is not a catalogue to be worked through, but examples to be derived on a risk basis.
Subsection 2 supplies the yardstick: on the basis of the national risk analyses and the operator's own risk analysis and risk assessment, proportionate technical, security-related and organisational measures must be taken. The state of the art should be observed. Overall, a proportionality test applies in which the effort to prevent or limit an outage is weighed against the risk of an incident; economic aspects, including the operator's financial capacity, must be taken into account[3].
Under subsection 4 you must set out the measures in a resilience plan and apply it. The plan must show the considerations on which the measures are based, and it must refer to the operator's risk analysis and risk assessment[3]. This is exactly where audit-readiness is decided: a measure whose derivation from the risk analysis is not documented will not withstand a query from the supervisory authority under Section 16.
What the IT service provider does not cover
The most common misconception around the KRITIS Umbrella Act is that the cyber duty has already been dealt with, and with it the physical one. The act itself explicitly distinguishes the two protection domains: IT security requirements are regulated as part of the transposition of the NIS2 Directive, while the KRITIS Umbrella Act sets, for the first time, independent, federally uniform, cross-sector minimum requirements for the physical protection of critical facilities.
The link runs in one direction: operators of critical facilities under the KRITIS-DachG are, as a rule, deemed particularly important entities under Section 28(1) no. 1 BSIG and are subject to the relevant BSIG duties. The reverse does not hold: not every company that falls under the BSI Act also falls under the KRITIS-DachG, because the scope of the BSIG is considerably wider.
- An ISMS or an IT-Grundschutz certificate replaces neither the threat and risk analysis nor the resilience plan for physical security
- The interfaces between physical security and information security must be known and taken into account in the concepts, for example in access control and network infrastructure
- The physical duties under Section 13 KRITIS-DachG must be fulfilled separately and evidenced separately to the supervisory authority, for example by submitting the resilience plan or through audits under Section 16[4]
For how you commission work, this means: check which services your IT service provider covers contractually. Its mandate typically covers IT security under the BSIG, but not the threat and risk analysis for sites, the derivation of protection zones, or the specialist planning of perimeter security, video surveillance and access control. This physical side is a planning field of its own with its own evidence duties.
Who prepares the threat and risk analysis and what it must contain
The legal framework is set out in Section 12 KRITIS-DachG: on the basis of the national risk analyses and other trustworthy sources of information, the operator carries out a risk analysis and risk assessment as required, but at least every four years. The Federal Ministry of the Interior is empowered to specify content and methodological requirements, including templates and models, for these analyses[5]. The duty therefore always lies with the operator; it can organise the preparation internally or externally.
What matters is not who writes the analysis, but that it survives an audit. That requires the derivation to be documented without gaps and the proportionality assessment under Section 13(2) to remain traceable. An analysis with audit-ready content contains at least:
- A systematic record of the threats to the site and the critical facility, including dependencies on other critical services under Section 12(1)[5]
- Definition of the protection objectives for each facility and area
- Protection zone concepts that divide the site into protected areas with graded requirements
- A catalogue of structural, technical and organisational measures
- A documented weighing of ends and means as a target concept, to which the resilience plan under Section 13(4) can refer[3]
Whether to do it internally or externally comes down to three criteria. Does your organisation have specialist staff who can derive threat and risk analyses for security technology with methodological rigour? Is the internal derivation independent enough, that is, free from the requirements of a supplier or installer? And will the documentation withstand an audit by the supervisory authority or an independent third party? Where one of these criteria is not met, external preparation is the more economical route. PLANATEL® prepares such threat and risk analyses and security concepts for KRITIS operators, among others in energy supply, municipal drainage and aviation, and derives every measure from the analysis with documentation (Security Concepts & Threat Analyses).
Finally, note the level of responsibility above that: under Section 20 KRITIS-DachG, management is obliged to implement the resilience measures and to ensure their implementation through suitable organisational measures. Responsibility for compliance lies explicitly at management level. The threat and risk analysis is therefore also management's basis for decision-making.
From analysis to implemented measure
The threat and risk analysis names the risk and prioritises the measures. Implementation itself requires specialist planning: the catalogue of measures becomes a technical concept in which the individual trades are planned in coordination with each other, not side by side. For critical sites this typically includes:
- Perimeter security as the first protection zone at the site boundary
- Video surveillance for monitoring the surroundings and documenting incidents
- Access control and locking technology for the access controls under Section 13(3) no. 2[3]
- Intrusion detection systems for detection in monitored zones, matched to the requirements of a police connection (Intrusion Detection, Video Security & Access Management)
- Fire alarm systems and voice alarm systems, where they form part of the facility's protection and evacuation concept (Fire Alarm, Voice Alarm & BOS Emergency Radio)
- Integration of all trades into a higher-level security management system and the control room, so that incidents are detected, reported and handled consistently (Security Management Systems (PSIM) & Control Rooms)
The route from concept to technology should run through a manufacturer-independent tender. A specification of services on which installers can bid makes offers comparable and avoids manufacturer lock-in, which becomes expensive over the life of the installation. Site supervision through to acceptance ensures that the installed system matches the planned target and provides the documentation you can submit to the supervisory authority as evidence under Section 16[4].
This very chain, from the threat and risk analysis via the target concept and the manufacturer-independent tender through to acceptance, is the subject of our service Critical Infrastructure (KRITIS). There you will find how we prepare security concepts and threat and risk analyses, plan perimeter security, video surveillance, access management and intrusion detection technology, and integrate them into higher-level security management systems, always manufacturer-independent and committed to your protection objectives. Contact us for a no-obligation initial consultation. PLANATEL®: Independent planning and consulting since 1992. Tel: 040 / 23 73 02-30 | Email: info@planatel.de
Frequently Asked Questions
When did the KRITIS Umbrella Act enter into force?
The KRITIS Umbrella Act entered into force on 17 March 2026, after it was adopted by the Bundestag on 29 January 2026 and approved by the Bundesrat on 6 March 2026. It transposes the CER Directive (EU) 2022/2557 into German law and, for the first time, creates federally uniform minimum requirements for the physical resilience of critical facilities.
By when must operators of critical facilities be registered?
Operators must register with the Federal Office of Civil Protection and Disaster Assistance no later than three months after their facility is deemed critical. Important: the originally stated date of 17 July 2026 was struck by an amendment of 29 July 2026, because the ordinance determining critical facilities has not yet been issued. The period therefore only starts when this ordinance enters into force.
Which deadlines apply after registration?
Under Section 8(7) KRITIS-DachG, the risk analysis duties first apply nine months after registration, and the duties concerning resilience measures, reporting and management first apply ten months after registration. After that, the risk analysis must be updated at least every four years, and earlier in the event of significant changes.
What does Section 13 KRITIS-DachG require of the operator?
Section 13 obliges operators to take proportionate technical, security-related and organisational measures to prevent incidents, ensure appropriate physical protection, respond to incidents and swiftly restore the critical service. Possible measures include structural and technical security, property protection, monitoring of the surroundings, detection devices and access controls. All measures must be documented in a resilience plan together with the considerations behind them.
Does IT security under the BSI Act or NIS-2 fulfil the physical duties?
No. The BSI Act and the NIS-2 Implementation Act govern IT security; the KRITIS Umbrella Act sets independent minimum requirements for physical protection. An ISMS or IT-Grundschutz certificate replaces neither the risk analysis nor the resilience plan for physical security. Conversely, operators of critical facilities under the Umbrella Act are, as a rule, deemed particularly important entities under Section 28 of the BSI Act.
Who prepares the risk analysis for physical security?
Responsibility lies with the operator; the analysis can be prepared internally or by an external, manufacturer-independent specialist planner. What matters is that the derivation of every measure from the threat and risk analysis is documented and defensible to authorities and expert assessors. Independent preparation ensures that the measures follow the risk, not a supplier's product catalogue.
What sanctions apply for breaches of the KRITIS Umbrella Act?
Breaches of registration, evidence and cooperation duties can be punished as administrative offences with fines, the amount of which depends on the specific offence. Management is also obliged to implement the resilience measures and to ensure their implementation through suitable organisational measures.
Sources
- KRITIS-Dachgesetz: Was Unternehmen jetzt wissen und tun müssen – IHK Köln
- § 8 KRITISDachG – gesetze-im-internet.de
- § 13 KRITISDachG – gesetze-im-internet.de
- § 16 KRITISDachG – gesetze-im-internet.de
- § 12 KRITISDachG – gesetze-im-internet.de
- KRITIS-Dachgesetz: Was Unternehmen jetzt beachten müssen – TÜV NORD
- KRITIS-Dachgesetz – OpenKRITIS
- KRITIS-Dachgesetz: Neuer bundeseinheitlicher Rechtsrahmen für den physischen Schutz kritischer Infrastrukturen tritt in Kraft – GÖRG